
The internet contains countless names, brands, domains, usernames, and online identities. Some become associated stash patrick with legitimate businesses and communities, while others appear in discussions about cybersecurity, underground marketplaces, or online fraud. Stash Patrick, sometimes written as Stashpatrick, is a name that may attract attention in searches related to underground online activity and payment-card discussions.
Understanding a name like Stash Patrick requires some caution. An online name alone does not establish that a website, service, stashpatrick.cc or organization is legitimate, safe, active, or officially connected to any particular operator. Online identities can be copied, changed, abandoned, or used by unrelated individuals.
For this reason, the most useful way to examine the Stash Patrick name is through the broader topics of online security, digital privacy, underground marketplaces, and responsible internet use.
What Does the Stash Patrick Name Refer To?
Stash Patrick is a name that can appear in online discussions concerning underground digital marketplaces and payment-related cybercrime. The spelling may also appear in variations such as Stashpatrick.
However, online references can be difficult to verify. Underground services frequently change their names, domains, and communication methods. Some websites may also imitate recognizable names to attract visitors or collect sensitive information.
As a result, users should not assume that every website or social-media account using the Stash Patrick name is connected to the same entity.
This distinction is especially important when researching unfamiliar websites. A search result, forum post, or advertisement is not sufficient evidence that a service is authentic.
Why Names Associated With Underground Markets Attract Attention
Underground online marketplaces have received considerable attention because they can be connected with cybercrime, stolen information, fraud, and other illegal activities.
Some criminal communities attempt to operate anonymously or conceal their infrastructure. This can make them difficult for ordinary users to evaluate.
Payment-card information is particularly sensitive. Criminals may attempt to obtain card details through phishing, malware, data breaches, or social engineering and subsequently distribute stolen information through illicit networks.
Consequently, names associated with payment-card marketplaces can attract attention from cybersecurity researchers, journalists, financial institutions, and law-enforcement agencies.
Stash Patrick and the Broader Cybersecurity Landscape
Rather than focusing only on a particular name, cybersecurity professionals generally examine the larger ecosystem surrounding underground activity.
This ecosystem can include stolen credentials, phishing campaigns, compromised accounts, malware, fraudulent websites, and payment-related attacks.
Understanding these patterns helps security teams identify risks before they affect customers or employees.
For example, if a company’s employee credentials appear in a known data breach, the organization can encourage password changes and strengthen authentication controls.
Similarly, if customers receive phishing messages imitating a financial institution, security teams can issue warnings and investigate the associated infrastructure.
The value of cybersecurity research therefore comes from identifying threats and improving defenses.
Why Online Names Can Be Misleading
Internet users should remember that names and domains can be misleading.
A fraudulent website may copy the name of a known service. An unrelated person may register a similar domain. A previously legitimate website may also change ownership or become inactive.
This is why users should not rely solely on branding when deciding whether an online service is trustworthy.
Important questions include who operates the service, whether the organization can be independently verified, whether legitimate contact information exists, and whether reputable sources recognize the service.
For financial activities, verification is especially important because sensitive information may be involved.
Risks of Interacting With Suspicious Websites
Visiting or interacting with suspicious online services can create several risks.
One risk is phishing. A fraudulent website may attempt to collect usernames, passwords, card numbers, or other personal information.
Another risk is malware. Some websites may attempt to persuade visitors to download files or install software that compromises their devices.
Scams are another concern. A website may request payment while failing to provide the advertised service.
There can also be legal consequences when a service is explicitly connected to criminal activity.
These risks make it important for users to avoid questionable marketplaces and rely on legitimate providers for financial and commercial services.
Protecting Personal Information
One of the most important lessons from discussions surrounding underground marketplaces is the value of protecting personal information.
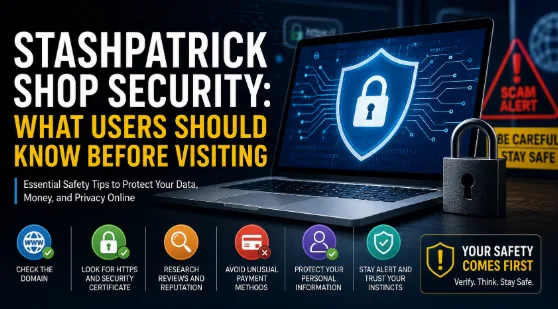
Consumers should avoid sharing passwords, payment credentials, identity documents, or security codes with unknown websites.
Passwords should be unique for important accounts. Reusing a password across multiple services creates additional risk because a breach at one website may expose access to other accounts.
A password manager can help users create and store strong credentials without needing to memorize every password.
The Importance of Multi-Factor Authentication
Multi-factor authentication provides an additional layer of account protection.
Instead of relying only on a password, the system requires another form of verification. This may involve an authentication application, security key, biometric verification, or another approved method.
If a password is stolen through phishing or a data breach, multi-factor authentication can make unauthorized access more difficult.
Users should enable this protection for important accounts, especially email, banking, payment, and business services.
Recognizing Phishing Attempts
Phishing is one of the most common techniques used to steal online credentials.
An attacker may send a message pretending to represent a bank, retailer, technology company, or payment provider. The message may claim that an account needs verification and provide a link to a fraudulent website.
Users should be cautious when unexpected messages request passwords, payment details, or verification codes.
Rather than clicking an unsolicited link, users should independently access the organization’s official website or application.
How Businesses Can Respond
Businesses can reduce risks associated with underground data markets by adopting strong cybersecurity practices.
Organizations should monitor for compromised credentials, maintain updated systems, restrict access to sensitive information, and require strong authentication.
Employee training is also important. Staff should understand phishing, suspicious attachments, social engineering, and procedures for reporting security incidents.
Companies should maintain an incident-response plan so that security teams can respond quickly when suspicious activity is discovered.
The Role of Threat Intelligence
Threat intelligence helps organizations understand emerging cyber threats.
Security researchers may monitor reports about compromised credentials, malware campaigns, phishing infrastructure, and underground criminal activity.
The purpose of responsible threat intelligence is defensive. Information about cybercrime can help organizations identify weaknesses and protect customers.
Financial institutions may use similar intelligence to improve fraud detection and identify emerging payment-related threats.
Responsible Research Into the Stashpatrick Name
Anyone researching the Stash Patrick or Stashpatrick name should prioritize reputable cybersecurity information rather than relying on anonymous advertisements or underground forums.
Security companies, law-enforcement agencies, academic researchers, and established technology publications may provide more reliable information about cybercrime trends.
Researchers should also avoid interacting with illicit services simply to investigate them. Responsible research can often be conducted through published reports and other legitimate sources.
What Consumers Should Remember
The most important lesson is that an unfamiliar online name should never automatically be treated as trustworthy.
Before using any financial or commercial service, consumers should verify the provider independently, examine its security practices, and avoid sharing unnecessary personal information.
Users should also monitor financial accounts for unusual activity and report suspected fraud to the relevant institution.
If an account may have been compromised, changing the password and enabling multi-factor authentication can help reduce further risk.
Conclusion
Stash Patrick, also referred to as Stashpatrick in some online contexts, is a name that may appear in discussions involving underground marketplaces and payment-related cybercrime. Because online identities and domains can be changed, copied, or impersonated, individual references should be treated carefully rather than automatically regarded as evidence of legitimacy.
The broader topic provides an important lesson about digital security. Underground marketplaces can be associated with stolen information, fraud, phishing, malware, and other risks. Consumers and businesses can reduce exposure by using legitimate services, protecting account credentials, enabling multi-factor authentication, monitoring financial activity, and learning to recognize suspicious online behavior.
Understanding names associated with underground activity is ultimately most useful when that knowledge is applied defensively. Good cybersecurity practices can help users protect their privacy, financial information, and digital identities in an increasingly connected online environment.
